Security & Data Protection

Your data stays
yours. Always.

DEXA sees every deal on your book — so we built it to protect every one of them.
Read-only access to your platform, a separate database for every broker and no trader personal data by default, all run under an information security management system certified to ISO/IEC 27001:2022.

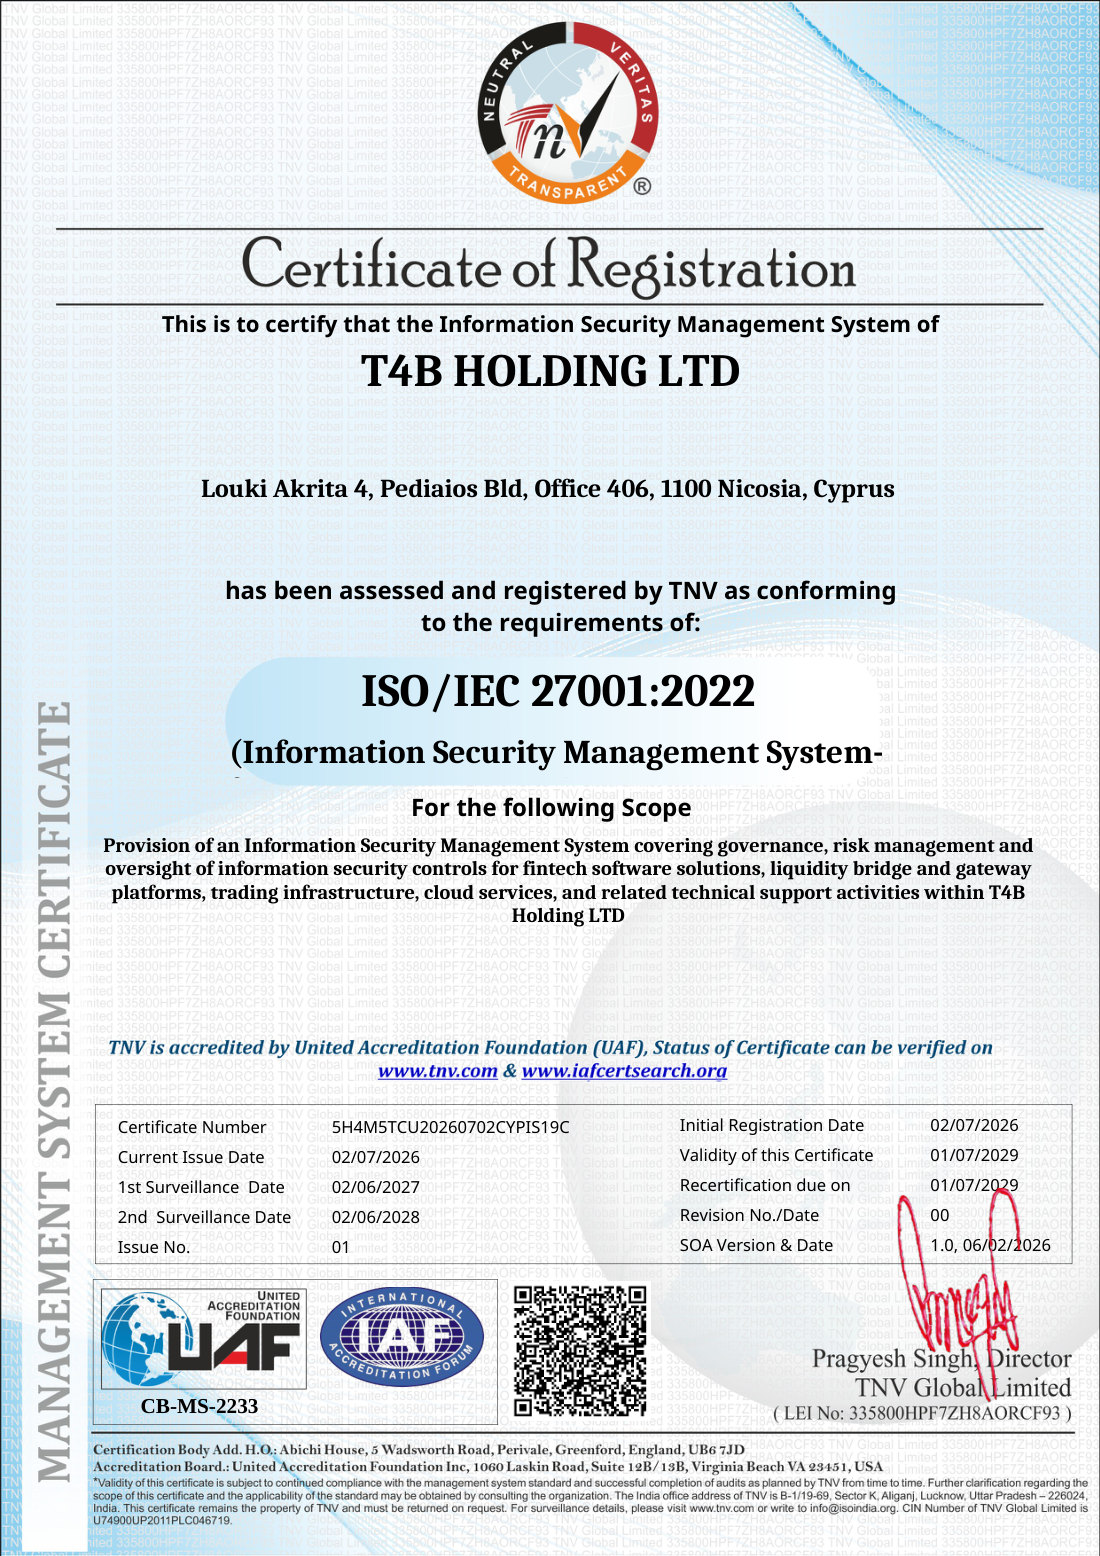
Certificate No. 5H4M5TCU20260702CYPIS19C · valid until 1 July 2029

93
Security controls assessed under our ISO/IEC 27001:2022 certification
1: 1
One isolated analytics database per broker
0
Trader names, ID documents or bank details needed to run the analytics
256-bit
AES encryption for your platform credentials at rest
Our principles

Six promises built into the code,
not just into the contract.

Security at DEXA isn’t a document written after the fact. It’s how the platform is engineered: each of these is enforced by the system itself, on the server, for every request.

01 · Observe, don’t touch

Read-only by design

DEXA reads your book through a read-only database connection or your platform’s reporting API. Analytics can’t open, close or modify a single trade.

The only changes DEXA ever makes on your servers are automation actions you configure yourself — through a limited Manager account that you create and control.

02 · Isolation

One broker, one database

Your deals, positions and trader profiles live in an analytics database of their own — physically separate from every other client’s.

On top of that, every request is bound to your workspace on the server side, so nobody outside your team can query your data.

03 · Data minimisation

No personal data by default

Classification, risk and A/B-book analytics run on trading behaviour alone. DEXA doesn’t need your traders’ names, ID documents, KYC files or bank details — so it doesn’t collect them.

Want names on screen? You switch them on, server by server.

04 · Encryption

Encrypted in transit and at rest

Traffic between your browser and DEXA, and between DEXA and its databases, is protected with TLS.

Your platform logins, passwords and server addresses are stored AES-256 encrypted. User passwords are hashed with bcrypt — never stored or logged in plain text.

05 · Access control

You decide who sees what

Every page can be set to Not allowed, Read only or Full access for each user — and the rule is enforced by the server, not just hidden in the interface.

Two-factor authentication with an authenticator app is built in, and it is mandatory for external dealing teams you invite.

06 · Responsible AI

AI with no direct access

The AI never connects to your database. It can only propose a query — DEXA checks it for safety first and only then runs it on the AI’s behalf:

  • Anything that could change data, read system tables or reach external systems is blocked before it runs
  • Approved queries run read-only, in your database only
  • No access to trader names, emails or comments
  • Strict time and row limits; the AI gets back only a capped extract

Your data is never used to train third-party AI models.
Tenant isolation

Separate databases.
Not just separate logins.

Many SaaS platforms keep every client in the same tables and rely on a filter to tell them apart. DEXA gives every broker an analytics database of its own, so your flow never shares storage with anyone else’s — including your competitors’.

Least privilege, end to end

DEXA asks only for read access to your platform. Even inside DEXA, AI reports run under a restricted database user with fewer rights than the application itself.

Scoped on the server

Every API call is bound to your workspace before it reaches a database. A user of one broker has no path to another broker’s data.

Dedicated when you need it

Larger brokers can run on their own dedicated database servers and sync workers.

Data minimisation

We analyse trading behaviour.
Not people.

Personal data that the analytics don’t need simply never enters DEXA. Less data stored means less data that could ever be exposed — and a much simpler conversation with your regulator and your DPO.

What DEXA works with

Trading data — everything the analytics need.

  • Trading account numbers, groups and leverage
  • Deals, orders, positions and balance operations
  • Balance, equity, margin and exposure
  • Symbols, prices and timestamps
  • Connection data such as IP addressesUsed only to detect multi-accounting and abuse

What DEXA never needs

So it isn’t collected in the first place.

  • Passports, ID documents and KYC files
  • Bank accounts, cards and payment details
  • Phone numbers and home addresses
  • Your traders’ platform passwords
  • Trader namesOff by default — see below

Optional, and always your call. Two things are off unless you switch them on: showing trader names (the “Load traders personal data” setting, per trading server) and linking a client’s accounts by email. Switch names off again and they are wiped from DEXA on the next full sync.

Enterprise · On-premise by request

Keep your data
on your own servers.

For enterprise clients we offer an on-premise deployment. The database with all your broker data and the servers that process it run inside your infrastructure, under your control. The web interface stays on our side, in the DEXA cloud, which keeps only platform-wide settings and the configuration of your DEXA environment.

  • Stored and processed on your serversIn your own data centre or your own cloud account
  • Your perimeter, your rulesYou decide on network access, backups, retention and who can reach the servers
  • Easier conversations with your regulatorHelps meet data-residency and outsourcing requirements
  • Planned with your IT teamSizing, deployment and connectivity agreed together, project by project
Your infrastructure Your control
DEXA database

All your broker data: deals, positions, balances, trader profiles, classifications and reports

DEXA processing servers

Synchronisation, classification, risk monitoring and report generation

Your trading platform

Already in your perimeter — your trading data is processed right next to it

DEXA cloud Interface & settings
Platform settings

General configuration of the DEXA platform

Your DEXA environment

Users, roles, rules and connection settings

DEXA web interface

The app your team signs in to — hosted and kept up to date by us

Your team keeps signing in to the same DEXA app. When a page opens, its results are fetched from your servers over an encrypted connection to be displayed.

Independent certification

Certified to ISO/IEC 27001:2022.

ISO/IEC 27001 is the international standard for information security management. Our certificate means independent auditors have examined how we govern risk, control access, manage suppliers and handle incidents — and that they come back every year to check again.

ISO/IEC 27001:2022 Certificate of Registration issued by TNV Global Limited to T4B Holding Ltd, certificate number 5H4M5TCU20260702CYPIS19C Valid until 1 July 2029

The whole company behind DEXA is in scope — not just one team.

DEXA is built and operated by the Tools For Brokers group of companies (T4B). The information security management system of T4B Holding Ltd covers our fintech software, trading infrastructure, cloud services and the technical support we provide to you.

Certified scope

“Provision of an Information Security Management System covering governance, risk management and oversight of information security controls for fintech software solutions, liquidity bridge and gateway platforms, trading infrastructure, cloud services, and related technical support activities within T4B Holding LTD.”

Standard
ISO/IEC 27001:2022
Certificate holder
T4B Holding Ltd
Certification body
TNV Global Ltd (UAF-accredited)
Certificate No.
5H4M5TCU20260702CYPIS19C
First registered
2 July 2026
Valid until
1 July 2029

Risk-driven

Information security risks are identified, assessed and treated formally — not ad hoc.

93 controls reviewed

Every control in the 2022 standard is assessed in our Statement of Applicability.

Audited every year

Surveillance audits in 2027 and 2028, full recertification in 2029.

Continuously improved

Incidents, audits and reviews feed back into how we work.

Day-to-day security

Secure on day one.
And on day one thousand.

Certification is the floor, not the ceiling. This is how we keep DEXA safe between audits.

Need-to-know access

Production systems are reachable only by a small group of authorised engineers. Internal operations tools are separate from the broker app and never exposed to clients.

Protected at the edge

All public traffic passes through a global edge network with built-in DDoS protection before it ever reaches our servers.

Monitored around the clock

Connectors, syncs and databases are health-checked automatically, with alerts routed straight to our engineers.

Tested before every release

More than 27,000 automated tests — over 15,000 unit tests and over 11,000 end-to-end checks — must pass before a release reaches production.

Incident response

A documented incident process. If a security incident ever affects your data, we tell you without undue delay — what happened, what was affected and what we’re doing about it.

Retention and clean exit

Retention periods are applied automatically. If you leave, you get a 30-day window to export, after which your database is deleted.

Questions from compliance teams

The questions your DPO will ask.

Does DEXA need write access to my trading server?
No. Analytics only need a read-only connection to your platform’s database or reporting API. A limited Manager account is optional and only used for automation actions you set up yourself — for example moving a trader to another group. Nothing runs on your servers unless you configured it.
Can another broker ever see my data?
No. Your analytics live in a database of their own, and every request is bound to your workspace on the server side. Nothing is shared with or visible to any other DEXA client.
Can DEXA run on our own servers?
Yes — for enterprise clients, on request. The database with all your broker data and the servers that process it run inside your infrastructure and under your control, while the web interface, platform settings and your environment configuration stay in the DEXA cloud. More about on-premise.
Do you sell, share or advertise with our data?
Never. We don’t sell client data, we don’t use it for advertising or profiling, and we share it with sub-processors only as far as needed to run the service — for example hosting providers. The full picture is in our Privacy Policy.
Is our data used to train AI models?
No. AI-assisted reports use commercial AI APIs that do not train on your data. The AI receives only what it needs to answer a question, through a restricted read-only database user — and never sees trader names, emails or comments.
Who is the data controller under GDPR?
You are. DEXA acts as a processor and handles your data only on your documented instructions. We support you with data-subject requests and anything else your compliance team needs.
What happens to our data if we stop using DEXA?
Your workspace is kept for 30 days, so you can export what you need or change your mind. After that, your database is deleted under our standard retention process.
Can you help with our vendor due-diligence questionnaire?
Yes. Send it to [email protected] — our team will answer it and share our ISO/IEC 27001 certificate and data-processing terms.